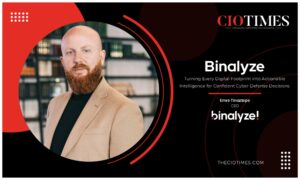
Cybersecurity has emerged as a crucial pillar of enterprise success. Pioneers in the sector help organizations build resilience in an environment where threats are constantly evolving. Their focus extends beyond preventing attacks to creating secure digital foundations that support growth, inspire customer confidence, and strengthen long-term business performance. A similar company is Binalyze, as the company’s deep technical expertise makes it stand out from others. The organization’s role is not limited to strengthening digital trust. The team has an unwavering focus on safe, resilient, and future-ready enterprises.
Decoding Cyber Truth
The organization helps security teams move beyond detection to uncover the truth behind cyber incidents. While security tools generate alerts, they rarely explain how an attack unfolded. The AIR platform delivers the investigative context needed to answer these critical questions, enabling faster, more informed incident response. Trusted by enterprises and incident response providers globally, the organization is helping redefine cyber investigation by turning alerts into answers.
Investigation First
“One day, something is going to get through. Then what?
Emre Tinaztepe, CEO
Binalyze has built its reputation in digital forensics and incident response by challenging conventional approaches to cybersecurity. While the industry has traditionally prioritized prevention and detection, the company recognized that neither provides the complete picture. As cyber threats continue to evolve, understanding what actually happened after an incident has become just as critical as identifying that one occurred.
This belief has shaped the organization’s vision from the outset. The company observed that investigation teams were spending valuable time on manual evidence collection, navigating disconnected tools, and reconstructing events before meaningful analysis could begin. The team set out to transform the investigation process itself.
As today’s organizations generate unprecedented volumes of alerts, telemetry, and security data, the company believes that more information does not necessarily create greater clarity. Instead, the team advocates making investigation a core component of everyday security operations rather than a reactive process reserved for major breaches. While detection highlights that an incident may have occurred, investigation uncovers the complete story, a distinction the company believes is redefining the future of cybersecurity.
Evolving Threats
The greatest challenge organizations face today is the increasing complexity of modern attack environments. Threat actors are becoming more sophisticated, leveraging legitimate credentials, trusted tools, and cloud services to blend into everyday operations and evade traditional detection.
At the same time, enterprises are managing vast, interconnected ecosystems that generate unprecedented volumes of security data. While visibility has improved, context often remains elusive. The real challenge is determining the alerts’ significance. The company believes this shift is evaluating the role of investigation in modern cybersecurity. Organizations must move beyond detection to understand how an attack unfolded, assess its true impact, and establish with confidence that the threat has been contained. The team sees this investigation-first approach as the future of effective cyber defense.
Intelligent Response
Binalyze strengthens existing security ecosystems by focusing on what happens after a threat is detected. Rather than replacing technologies such as SIEM or XDR, the company helps organizations uncover the context behind security events, enabling faster and more informed investigations.
By automating evidence collection and correlating data across endpoints, cloud environments, and enterprise systems, the team eliminates much of the manual effort that slows incident response. This allows investigators to focus on analysis and decision-making rather than repetitive tasks. Effective cybersecurity is not defined by the number of alerts generated, but by how quickly security teams can uncover the truth and respond with confidence.
The Analytical Edge
Artificial intelligence is remolding cybersecurity on both sides of the battlefield. It changes the way digital forensics and incident response function. While the industry continues to debate whether or not AI will replace analysts, the organization has a say in this too. It considers the more crucial question is whether it can help professionals investigate with the judgment of experienced practitioners.
Expert investigators are distinguished by the questions they ask. It also includes the patterns they recognize and the decisions they make. That expertise is built through experience and can make it difficult to replicate. This philosophy underpins Fleet AI. The solution is designed to eliminate repetitive tasks, enabling analysts to focus on critical thinking and higher-value investigations.
Customer feedback has reinforced this approach. AI’s greatest value lies in enabling investigators to think differently and uncover deeper insights. As threat actors increasingly leverage AI, defenders need to do the same. The goal is to implement autonomous investigations, where AI amplifies human expertise instead of replacing it.
A Holistic Threat Visibility
Several organizations have had significant contributions in cybersecurity. They have built sophisticated security stacks and addressed evolving threats too. The challenge is fragmentation of security ecosystems for the team. Every solution provides valuable insights from its own perspective. It can include aspects like SIEM, EDR, identity, cloud security, or threat intelligence. The real challenge lies in connecting those insights to form a complete picture, making investigations slower and more complicated.
The organization often poses a simple question: how many tools must an analyst access before understanding what is actually happening? More often than not, the answer is too many.
Security teams need confidence. They need to determine whether an incident is genuine, whether it is contained, whether the threat remains active, and whether it is safe to move forward or not. These answers come from deeper understanding and expertise that has been gained from years of dedication. Closing that gap has been central to the team’s vision from the very beginning.
Workforce Intelligence
The global cybersecurity talent shortage remains a significant challenge. However, the team at Binalyze extends this solution beyond only hiring people. With experienced investigators in limited supply, they highlight the fact that organizations must rework how they strengthen security capabilities.
The organization’s philosophy is rooted in augmenting human expertise through technology. While machines excel at collecting data and automating repetitive tasks, people provide the context, judgment, and decision-making that effective investigations demand. By automating routine investigative work, analysts can focus on higher-value analysis and critical decision-making. This maximizes both efficiency and expertise.
The team also focuses on the untapped potential of junior analysts. These analysts lack context more than capability. Equipping them with better information, structured workflows, and intelligent guidance enables them to develop more quickly and contribute with greater confidence. This approach does more than address today’s skills shortage. It helps cultivate the next generation of experienced investigators while strengthening long-term cyber resilience.
Security Assurance
Regulatory requirements continue to evolve. Binalyze believes compliance is becoming increasingly practical and demands concrete solutions. With depleting dependency on documentation, it is now about exhibiting a clear understanding of the environment and the ability to respond effectively when incidents occur.
This is a positive shift as the team recognizes that effective compliance is of the same stature as security. When investigations are thorough, evidence is reliable, and processes are consistent, compliance becomes a natural by-product.
This philosophy has shaped the team’s approach. By automating evidence collection, preserving its integrity, and documenting investigations throughout the response process, the organization enables investigators and auditors to work more efficiently.
The team doesn’t address compliance as a post-incident exercise. It integrates it into daily security operations. Organizations increasingly seek solutions that integrate seamlessly into existing workflows. The goal is a clearer understanding of incidents and the confidence to demonstrate how they were handled. That is where security, operational efficiency, and compliance converge.
Strategic Resilience
Organizations often confuse cyber resilience with cyber prevention, the team points out. They are related closely, but they aren’t the same. There is a difference between the two. As threats, technologies, and business environments evolve, no security strategy can prevent every attack. Resilience is defined by understanding the incidents quickly and bouncing back with confidence.
The critical question and primary metric is: “At what point do you know the incident is actually over?” This requires understanding how the attacker gained success, what was compromised, whether access has been eliminated, and whether every vulnerability has been addressed. Without those answers, organizations are still relying on assumptions.
Emre Tinaztepe, CEO
This is why the Binalyze team views investigation as fundamental to cyber resilience. Effective investigations provide clarity, enabling organizations to respond decisively and recover with confidence rooted in understanding and not on assumptions.
Operational Simplicity
Innovation is the foundation of solving real challenges. At Binalyze, there is a consistency in asking thoughtful questions, recognizing that innovation is the art of turning complex challenges into elegant solutions. There is a consistency in asking thoughtful questions like:
1. Why do experienced investigators spend hours collecting evidence?
2. Why must analysts navigate multiple consoles to understand a single incident?
3. Why do organizations with robust security investments still struggle during investigations?
This problem-first approach has shaped the development of its solutions. The team shared an example of Fleet AI, which was established to address genuine investigative challenges. Rather than making decisions on behalf of analysts, it enables them to think faster, navigate investigations more efficiently, and reach critical evidence with greater speed.
The same philosophy guided the development of Outpost. As investigations increasingly span SaaS, containers, endpoints, cloud platforms, and remote environments, the organization hints that investigators should focus on the investigation, not on where the evidence resides. They should be able to collect trusted evidence efficiently and proceed with confidence.
All in all, the team’s innovation philosophy is simple: technology should reduce complexity, instead of contributing to it.
Efficient Security Decisions
Artificial intelligence will have an ardent impact on cybersecurity. Cloud adoption and identity security will continue to reshape the industry’s priorities. More significantly, the organization sees a shift from generating more security signals to understanding them more efficiently.
For years, cybersecurity has been measured by the speed of detection. Success will start depending on how quickly organizations can explain an incident. It includes:
What actually happened?
1. Validating the evidence
Communicating the findings to boards, regulators, and customers
2. Recovering with confidence
These are fundamental investigation challenges for the organization. These make investigation a core cybersecurity capability rather than a specialist discipline.
While AI will undoubtedly accelerate this evolution, the Binalyze team will enable organizations to understand incidents faster while reinforcing the importance of reliable evidence.
Committed to Excellence
While industry recognition is appreciated, the team believes its greatest achievement lies in helping customers solve complex investigations in a fraction of the time. The most meaningful validation comes when organizations gain a clear understanding of an incident.
The team’s success has been driven by a disciplined focus. Rather than attempting to solve every cybersecurity challenge, the team remains committed to advancing digital investigations with purpose and precision. That focus has fostered strong relationships with customers, partners, and investigators, whose insights continue to shape the organization’s evolution.
Speaking about the future, the organization promises to remain devoted to the same philosophy. Investments in AI, expanded investigation capabilities, and support for increasingly complex environments will remain key priorities. The broader mission remains unchanged: making investigations faster, simpler, and more accessible for security teams.
The organization believes informed decisions are built on clear understanding. Security teams are not lacking alerts; they are seeking confidence. Confidence in understanding an incident, identifying its root cause, and recovering effectively. By enabling that level of confidence, Binalyze continues to pursue the mission that has defined it from the beginning: not creating another security product, but a better way to uncover and understand the truth.
To learn more about Binalyze, visit: binalyze.ai
Also Read :- CIO Times Magazine For More Information